NGO Guide to Safe Analytics in Sensitive Regions
For most organizations, analytics is a marketing question. For an NGO operating where the government monitors civil society, it is a duty-of-care question. The same numbers that tell a donor whether a campaign reached two hundred thousand people can, collected carelessly, tell an intelligence service who read a report, when, from which neighborhood, and how often. This guide is about running honest web analytics in politically sensitive regions without creating a record that could ever be turned against the people you serve.
TL;DR
- Civil society is a documented surveillance target: the Pegasus Project traced spyware selection lists covering journalists, lawyers, and human rights defenders, and 2025 set a shutdown record of 313 incidents across 52 countries.
- Every analytics decision in a sensitive context reduces to one test: if this database were seized or subpoenaed tomorrow, could a row in it point at a person? Configure until the answer is no.
- The hardening checklist is short: cookieless tracking, IP addresses truncated before storage, country-level geography only, short retention, no server logs, no cross-site identifiers.
- A Europe-hosted or managed Matomo instance keeps visitor data out of in-country reach and under GDPR-grade protection at EUR 9 to EUR 22 per month.
- Donor reporting survives all of it: aggregate reach, campaign completion, and document downloads answer every funder question without a single visitor profile.
When analytics becomes a safety question
The scale of the problem is no longer speculative. Access Now's KeepItOn coalition documented a record 313 internet shutdowns across 52 countries in 2025, the highest count ever recorded and the third record year running. Targeted digital intrusion against civil society is equally documented: the Pegasus Project's leaked selection lists, verified by a consortium of dozens of media partners, included human rights defenders, opposition figures, lawyers, and journalists; US authorities later blacklisted the vendor and Apple sued it. None of that happens through the analytics tag on an NGO website. All of it establishes the operating reality: in sensitive regions, organizations that document abuses assume adversaries with technical capability and legal reach.
Website analytics sits lower on the threat list than a phone, but it deserves the same discipline, because analytics databases are unusually attractive: they are organized, timestamped, and full of behavioral detail. A request log or analytics row saying a particular IP address loaded the human rights report twelve times in the week before a raid is evidence of the kind no organization should ever possess about its readers.
What a standard analytics setup leaks
Run through what conventional analytics collects in a sensitive context. A third-party tracker operated by a US ad platform receives the visitor's IP address, the full page URL, the referrer, a device fingerprint, and a persistent identifier, then stores that combination for months under a foreign legal regime that includes national-security access powers. Regulators in Europe have ruled that arrangement unlawful for ordinary commercial sites. For an NGO whose readers include activists in the very countries being documented, it is a direct third-party exposure: the data leaves your control at page load.
Self-hosting does not automatically fix this. A Matomo instance in a local data center, logging full IP addresses with default retention, merely relocates the record to where a subpoena, a raid, or a compromised server can reach it most easily. The fix is configuration and jurisdiction, not just software choice.
The one-question threat model
Formal threat modeling intimidates small teams, so reduce it to a single operational test that fits every analytics decision: if this database were seized tomorrow, could any row point at a person? An IP address with timestamps points at a person. A persistent cookie ID combined with page history points at a person. A full URL carrying a query string from an email campaign can point at the specific recipient, because mail-merge links often embed a supporter ID. Aggregate counts point at nobody.
Every section below is that test applied to one layer of the stack. If a setting fails the test and no configuration makes it pass, the setting gets switched off. That is the whole method.
Hardening Matomo for hostile environments
Matomo reaches a defensible posture through configuration, and each item below is a setting, not a development project:
- Track without cookies: no identifier is ever stored on the visitor's device, so there is nothing to correlate across visits
- Truncate IP addresses before storage: Matomo can anonymize the address at collection time, so the database never holds the full value
- Limit geography to country level: city-level geo-location is derived from the IP and re-derivable if the address survives; country level answers reporting questions without the precision
- Set aggressive retention: raw visit data at the shortest window your reporting honestly needs, measured in weeks, not years
- Disable server log storage or rotate it daily, because web server logs capture full IPs by default and outlive every analytics setting
- Switch off visitor profile, cross-site linking, and any session recording feature before launch, not after
Configure all of it before the first real traffic arrives. Retroactive anonymization of data you never collected needs no cleanup.
Collecting nothing that identifies a source
Three collection paths betray readers by accident, and each has a clean fix. First, campaign URLs: mail-merge tools append supporter identifiers to links, and those identifiers land in your analytics as page URLs. Configure Matomo to exclude URL query parameters from tracking, and train the campaigns team to use parameter-free links for sensitive mailings. Second, referrer detail: a referrer from a private forum or an internal resource exposes where readers come from; a strict referrer policy on the site plus referrer cleanup in the tag limits what arrives. Third, on-site search terms: a reader searching your site for "asylum lawyer" or a village name is telling you something no database should hold. Disable site search tracking in sensitive contexts, always.
Where the organization needs logged-in supporter analytics, hash the user identifier before it reaches Matomo so the analytics store holds an irreversible token, never an email address. The donor privacy tracking guide covers that pattern for fundraising contexts in detail.
Program metrics that satisfy donors
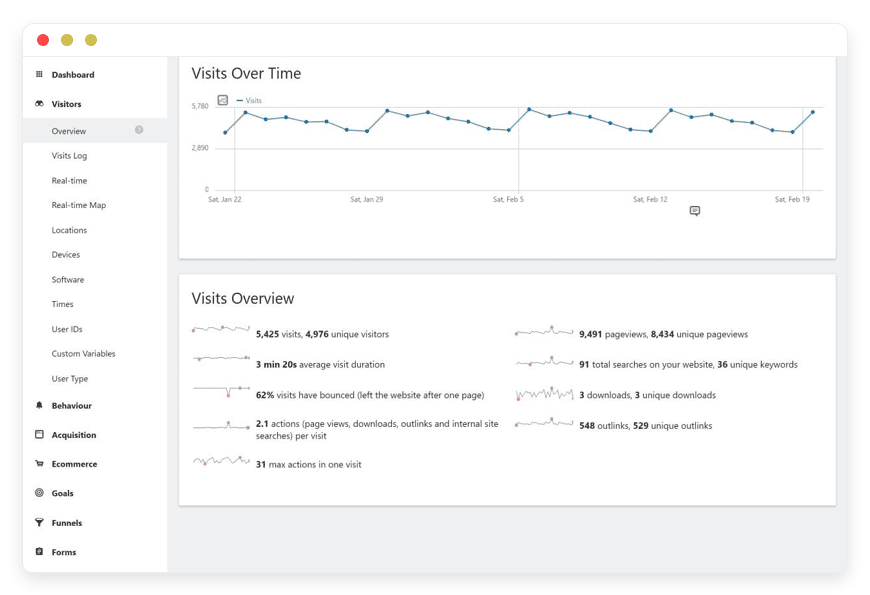
Foundations ask reasonable questions: did the campaign reach people, did the report get read, did the advocacy page drive action. Every one of those answers survives full anonymization:
- Page and report reads, aggregated by week and by country
- Campaign funnel completion: visited, scrolled, clicked through, signed or downloaded
- Document downloads per publication, per language
- Newsletter growth and churn as counts, never as profiles
- Trajectory over time, which is what funders fund
What disappears is the ability to say which specific person did which specific thing, and no honest funder asks for that. If a grant application demands individual-level web data, that is a conversation to have with the funder, and increasingly funders themselves publish responsible-data policies that expect you to refuse. For structuring the measurement side around campaigns rather than people, the nonprofit campaign tracking guide maps the events.
Where the data lives: jurisdiction decisions
Configuration controls what is collected; jurisdiction controls who can compel it. Three options, in ascending order of protection: hosting in the operating country keeps latency low and puts the database one administrative request away from the ministry you document. Self-hosting in Europe puts the data under GDPR-grade legal process, but your team carries every patch, backup, and incident. A managed Europe-hosted Matomo instance adds a professional operations team, encrypted backups, and a contractual data processing agreement at EUR 9 to EUR 22 a month, and for teams without a security engineer, that third option is the one that gets maintained properly past month three, because unpatched analytics software is its own seizure path.
Two practices complete the jurisdiction picture. Keep an export routine and a deletion runbook tested, so the organization can truly delete on demand rather than in theory. And document the whole configuration: regulators, auditors, and institutional funders increasingly accept that a written data-protection posture is part of an NGO's governance, and the documentation doubles as the onboarding manual when the person who configured it all leaves.
Access, accounts, and incident habits
The database is only as safe as the accounts around it. Require two-factor authentication for every Matomo login, keep the named-user list short, and review it when staff and volunteers rotate out, which in civil society they do constantly. Enable Matomo's audit log so administrative actions are attributable. Separate roles: the communications fellow who reads reports does not need configuration rights, and the intern does not need raw data export.
Rehearse the bad day before it happens. The runbook needs three entries: how to revoke access in minutes, how to delete a visitor dataset on demand, and who decides when a situation makes deletion the right call. Organizations that write this down in calm weeks make defensible decisions in bad ones. Pairs well with the wider responsible-data practices in the charities guide to managed analytics.
Frequently asked questions
Is cookieless analytics as accurate for reporting to funders?
For every question a funder asks, yes. Aggregate reads, downloads, campaign completion, and country-level reach are unaffected by removing identifiers. What becomes less precise is per-person journey analysis, which sensitive-region organizations should not be doing on the general public anyway.
Does an NGO need a cookie banner with this setup?
A cookieless configuration stores nothing on the visitor's device, which removes the trigger for banner consent in most frameworks, and several regulators in Europe describe an exemption for strictly limited audience measurement. Sensitive-region organizations often add a plain privacy statement anyway, because transparency with readers is part of the mission even when the law does not demand a popup.
Why not just use a privacy-friendly SaaS like Plausible or Fathom?
Those are legitimate options and lighter to run. The difference is control of the record: with a self-hosted or managed Matomo instance, the raw data sits in a jurisdiction you chose under an agreement you hold, and you can delete it completely on demand. For organizations whose adversaries include governments, keeping that lever matters more than convenience.
What if authorities demand data from our Europe-hosted instance?
A jurisdiction in Europe means lawful process, courts, and the ability to challenge orders, which is a different universe from an in-country server. A managed provider with a transparent policy will notify the organization where law allows. No configuration makes an organization immune to legal process; the goal is ensuring there is nothing personal in the database worth seizing.
How short should data retention be?
As short as honest reporting allows. Many teams find 6 to 13 weeks of raw visit data covers monthly and quarterly reporting cycles; aggregate report data can live longer because it contains no individuals. Review the window annually as reporting requirements change.
Can we still track newsletter and campaign performance?
Yes, as counts and completion rates. Use parameter-free or cleaned campaign links, disable site search tracking, and report on funnels rather than people. The campaign measurement recipes in the nonprofit tracking guide work unchanged under these settings.
Sources
- Access Now and the KeepItOn coalition, internet shutdowns in 2025 report, March 2026
- The Pegasus Project, Forbidden Stories and consortium partners, 2021
- US Department of Commerce action against NSO Group, 2021; Apple v. NSO Group filing
- Matomo privacy configuration documentation: anonymization, retention, cookieless tracking, matomo.org
- CNIL audience measurement exemption guidance
- The Engine Room, responsible data handbook for civil society