Fully Managed HeCAPTe
as a Service

Deploy HeCAPTe as a fully managed service starting at €9/mo. Get automated backups, SSL, updates, support and monitoring included.

HeCAPTe is a self-hosted CAPTCHA server that protects your forms from spam and bots: the browser solves a small proof-of-work puzzle silently, with no cookies, no tracking, and no image grids. It pairs the convenience of a hosted service like reCAPTCHA with the privacy and control of software you run yourself.

✓Free 7-day trial  ✓99.9% Uptime SLA  ✓No credit card  ✓Cancel anytime

✓Free 7-day trial  ✓99.9% Uptime SLA
✓No credit card  ✓Cancel anytime

HeCAPTe

HeCAPTe

STARTING AT

€9/month
Automated Backups
Monitoring
Automated Updates
Auto SSL

USAGE

Unlimited
Human Support
Custom Domains
Terminal Access
File Manager Access
Deploy in your region — 21 locations worldwide
GermanyFinlandNetherlandsUKSwedenUnited StatesCanadaSingaporeJapanAustraliaBrazilSouth Africa+9 more →
HeCAPTe Preview Image

ABOUT THE SOFTWARE

What is HeCAPTe

HeCAPTe is a self-hosted CAPTCHA server that protects forms from spam and automated abuse. Instead of profiling visitors, it asks the browser to solve a small proof-of-work puzzle: no cookies, no tracking, no images to click.

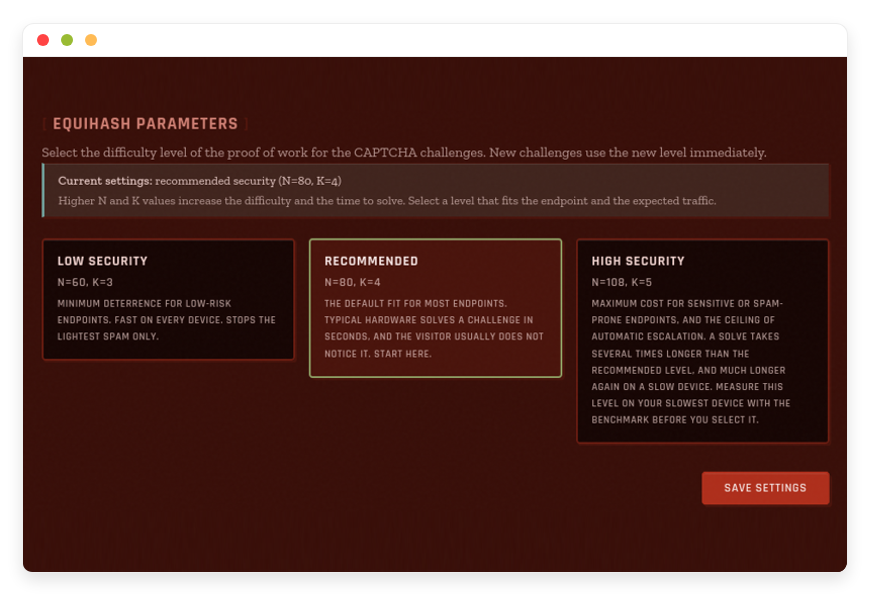
HeCAPTe is written in Go and ships as a single binary backed by a SQLite file, so it runs comfortably on modest hardware. The challenge the browser solves uses Equihash , a memory-hard proof-of-work algorithm (default parameters N=80, K=4): costly to solve in bulk but instant on an ordinary phone or laptop. The solver itself is compiled to WebAssembly and runs in a background worker, so the visible page stays responsive while the work happens.

The project is developed by Kat Suricata and released under the Mutualist License v1.2, a copyleft license with a network-use share-alike clause. The admin panel authenticates with passkeys (WebAuthn) and hashes credentials with Argon2id, and every challenge is HMAC-signed and checked against a shared replay store before it is accepted.

FEATURES

What HeCAPTe does

HeCAPTe is small on purpose: one Go binary, a SQLite file, and a browser-side solver. These are the capabilities of the software itself: the things it does once it's running on your forms.

Stateless proof-of-work challenges

Each challenge is an HMAC-signed bundle of salt, timestamp, and difficulty, verified in constant time with a 60-second expiry: no per-request database write and no server-side session to store.

WebAssembly browser solver

A small Go-compiled WebAssembly module solves each puzzle inside a Web Worker, keeping the visible page responsive while the proof-of-work runs in the background.

Memory-hard Equihash algorithm

Equihash needs memory to solve, not just raw compute, so attackers can't cheaply scale it on GPUs. A phone solves a puzzle about as quickly as a high-end laptop.

Replay protection

Used challenges are tracked in a shared replay store, the instance’s own SQLite database by default, and rejected on reuse, so protection survives restarts and works across replicas.

Per-site keys with origin allow-listing

The admin panel issues site-key and secret-key pairs, each with its own list of allowed origins, so one instance can protect many domains with separate rules.

Passkey admin login

The admin panel supports WebAuthn passkeys alongside passwords, with short-lived sessions and a separate re-authentication step for sensitive changes.

Three difficulty presets

Operators pick Low, Recommended, or High difficulty from the admin panel, trading visitor speed against spam cost, without rebuilding the server.

Built-in translations

Server-side internationalization detects the visitor's language from the Accept-Language header, with a query-parameter override; new languages are added by dropping in a translation file.

WHAT'S ALWAYS INCLUDED

Every app. Fully managed.
Nothing extra to pay for.

Every app on DANIAN ships with the same operational baseline. You do not choose a backup add-on or a monitoring tier. Hosting, patching, backups, SSL, and support are part of the €9, and they apply to HeCAPTe the same way they apply to everything else in the catalog.

Automatic updates and patches

Apps run the latest stable version. Security patches applied silently, with rollback if needed.

Daily off-site backups

Multiple daily backups in redundant off-site locations. One-click restore if anything goes wrong.

24/7 uptime monitoring

Continuous monitoring with instant alerting. We respond before you notice.

SSL, firewall, DDoS protection

Auto-renewing SSL, hardened firewall rules, DDoS mitigation on every deployment.

Performance and scaling

We monitor resource usage continuously. When your app needs more headroom, we flag it and upgrade with your explicit approval.

Dedicated engineering support

Real engineers by email and ticket. DNS, SMTP & migration help. All included in €9.

WHY MANAGED

Why teams pick managed HeCAPTe

In April 2026, reCAPTCHA's terms changed: the site operator, not Google, now carries the legal responsibility for the visitor data it collects, while the free tier was capped at 10,000 checks a month. Running your own CAPTCHA puts that data, and that cost, back under your control.

Self-hosting HeCAPTe is more than starting the binary. The server needs SSL, a reverse proxy configured correctly, a unique signing secret, off-site backups, monitoring, and someone to test each upstream release before it reaches production. HeCAPTe moves quickly: v4.0 shipped in September 2026 as a breaking release, so tracking the changelog is ongoing work, not a one-time setup.

One specific trap catches most self-hosters. HeCAPTe marks its admin session cookies Secure only when it can tell the connection is HTTPS, which, behind a reverse proxy, depends on the proxy sending the X-Forwarded-Proto header. Miss that header and admin login silently fails over HTTPS, with no obvious error to chase. We set it as part of provisioning, so it never becomes a late-night debugging session.

We run HeCAPTe the way it should be run. Every instance gets a unique signing secret generated from real randomness, the difficulty preset tuned to your traffic, the reverse proxy configured correctly, auto-renewing SSL, daily off-site backups, and 24/7 monitoring. We track upstream and pin your instance to a known-good build, so a fast-moving project stays boring on your side.

REVIEWS

Hear from customers ​like you​​​​​​​

Successful businesses and professionals around the world rely on DANIAN every day

USE CASES

Three teams who run HeCAPTe on DANIAN

HeCAPTe fits anywhere a form is under attack and visitor privacy matters. Three patterns we see often, with the configuration choices that make each one work.

4-PERSON SAAS TEAM

Protecting signup without sending data to a vendor

A small developer-tooling company guards its signup, password-reset, and contact forms, about 3,000 real submissions a month against tens of thousands of bot probes. One HeCAPTe instance behind a reverse proxy on the Recommended preset covers all three forms, with no visitor data leaving to a third party.

12,000-MEMBER FORUM

Pricing spammers out of mass registration

A community forum fights persistent automated sign-ups. They run the High difficulty preset on registration to make bulk account creation uneconomic, and keep posting on the Recommended preset so real members feel nothing. Allowed origins are locked to the forum's own domain.

DRUPAL STORE

Invisible checks on account creation and checkout

An online shop wires HeCAPTe into Drupal with the community module. The solver is proxied through the site's own routes, so no cross-origin requests are made and the content-security policy stays strict. Registration, password reset, and checkout account creation are all protected.

COMPARISON

Four ways to run HeCAPTe

There are four common ways to run a CAPTCHA like HeCAPTe. A hosted SaaS charges per domain and holds your data. Two self-hosted paths give you control but cost your time. Managed hosting keeps the control and removes the upkeep.

Approach~1 site~5 sites~10 sitesYou maintainData held by
Proprietary SaaSe.g. Friendly Captcha, priced per domain€9/mo€39/mo€200/moNothingThe vendor
Self-host on a VPSone ~$24/mo production-class server~$24/mo~$24/mo~$24/moEverything, plus your timeYou
Home or business serverfrom ~€650 once, plus powerhardware + powerhardware + powerhardware + powerEverything, plus hardwareYou
DANIAN managed HeCAPTeflat €9, any number of sites€9/mo€9/mo€9/moNothingYou

Friendly Captcha tiers: €9 (1 domain, 1,000 requests/month), €39 (up to 5 domains, 5,000 requests), €200 (up to 50 domains, 50,000 requests), from friendlycaptcha.com. A single HeCAPTe instance issues unlimited site keys, so one €9 DANIAN instance protects all your domains. The VPS path is one ~$24/month production-class server plus the setup and upkeep time you put in. Hosted incumbents like reCAPTCHA (free to 10,000 checks/month, then paid) and hCaptcha (Pro from $139/month) sit in the same proprietary-SaaS column.

BY INDUSTRY

HeCAPTe for specific industries

Different sectors put different demands on a CAPTCHA: accessibility rules, spam pressure, data-handling expectations. Here is how managed HeCAPTe is set up for five of them, with the configuration choices we make for each.

Privacy-first products want bot protection that collects nothing about visitors, in line with the data-minimization principle. HeCAPTe sets no cookies, makes no third-party requests, and stores no visitor identity, so a sign-up, login, or password-reset form is protected by an invisible check rather than a tracking widget. We run the Recommended preset (Equihash N=80, K=4) with IP logging off and no analytics hooks, and lock allowed origins to your application's own domains. The verification happens server-side against your instance, so your backend stays in control of the decision. The measurable result is zero cookies set on the visitor's browser and zero third-party requests made from your forms, which keeps your privacy notice short and your data flows entirely under your own roof.

Online stores need to stop fake accounts and carding bots on checkout and signup without adding friction for real shoppers, and many follow the WCAG 2.1 Level AA accessibility standard. We set the Recommended preset on checkout for low friction and the High preset (N=108, K=5) on account creation, where attackers concentrate. The proof-of-work runs in a background Web Worker while the shopper enters card details, and is verified server-side before the order posts, so the check never stalls the purchase. Because HeCAPTe presents no image grid and no audio challenge, it avoids the accessibility failures that checkbox CAPTCHAs trigger in an audit: there is simply no visual puzzle for a screen-reader user to fail. The result is fraud pressure priced out of bulk attacks while the checkout stays fast and accessible for everyone.

Forums fight persistent automated registration and comment spam, and spam handling is a documented operational concern for any platform hosting user content. We run the High difficulty preset on registration and the Recommended preset on posting, with allowed origins locked to the forum's own domain. The forum's CAPTCHA hook calls the challenge endpoint on form load and the verify endpoint on submit, so the integration sits inside the platform you already run. The core idea is cost-asymmetry: HeCAPTe does not try to detect bots, it makes every submission cost memory-hard work. At the High preset, ten thousand spam registrations cost the attacker ten thousand rounds of Equihash, which makes mass sign-up uneconomic rather than merely flagged. Real members, submitting one form at a time, never notice the puzzle ran.

Public bodies and nonprofits often must meet the WCAG 2.1 Level AA and Section 508 accessibility standards, and want to avoid sending citizen data to outside vendors. We run the Recommended preset, host your instance in the region you choose, and use no third-party JavaScript at all. Forms on application and contact pages call your own instance, and nothing about the visitor leaves to an external service. Because there is no image puzzle, the check does not become an accessibility barrier on a benefits or grant application that has to work for every citizen. The measurable result is zero visitor data sent to any third-party analytics or scoring service, which sidesteps the international-transfer questions that data-protection regulators have repeatedly raised about telemetry-based CAPTCHAs.

Fintech signup needs to block automated account farming before any identity step, and downstream flows often require Strong Customer Authentication. We run the High preset on signup so bulk account creation is uneconomic, and HeCAPTe guards the pre-identity stage while your KYC process handles identity later in the flow. The check sits in front of registration, not inside the payment path, so it adds protection without touching the authentication your regulator cares about. Following OWASP password-storage guidance, HeCAPTe's admin layer hashes credentials with Argon2id at 128 MB of memory and 3 iterations, matching OWASP's recommended settings rather than an arbitrary default, and the admin panel supports passkeys for login. The result is a hardened front door on signup that keeps automated abuse out before your identity checks even run.

FAQ

Frequently asked questions

Three groups of questions: how HeCAPTe works and how we configure it, how to move over and get set up, and how billing, support, and the platform work.

01

Technical and configuration

No. The visitor's browser silently solves a small proof-of-work puzzle in a background worker. There is nothing to click, no images to identify, and no audio fallback. Most visitors never know a check ran at all.
Yes. The browser downloads a small solver compiled to WebAssembly and runs it in a Web Worker. A visitor with JavaScript disabled won't produce a valid token, so their submission is rejected server-side rather than waved through.
Equihash is a memory-hard proof-of-work algorithm. It is costly to solve in bulk because it needs memory, not just raw GPU compute, so a spammer can't cheaply farm it out. An ordinary phone solves a puzzle about as fast as a high-end laptop.
It doesn't try to identify them. Instead of profiling visitors, it makes every form submission cost CPU time. At the higher difficulty presets, sending thousands of spam submissions becomes more expensive than the spam is worth, so attackers move on.
We start most instances on the Recommended preset (Equihash N=80, K=4), which is invisible to real users. For an endpoint under active scraping pressure, we move that form to the High preset (N=108, K=5) and leave low-friction pages alone.
We make sure the proxy in front of your instance sends the X-Forwarded-Proto header correctly, so admin session cookies are marked Secure. A self-hosted setup that misses this header silently breaks admin login over HTTPS; we set it as part of provisioning so it never becomes a debugging session.
Every instance gets a unique signing secret generated from 32 bytes of real randomness, never the development placeholder shown in the docs. We store it outside the application and rotate it on request. The server refuses to start without one.
Yes. One HeCAPTe instance issues multiple site-key and secret-key pairs, each with its own allowed-origins list. You can protect many domains from a single €9 instance, with separate rules per site.
HeCAPTe verifies challenges in constant time with no per-request database write, and tracks used challenges in memory to block replays. We monitor the instance and scale its resources if your traffic outgrows the base tier, after talking to you first.

02

Migration and onboarding

21 datacenter locations across six continents. You choose the region at provisioning. Application data sits in the region you choose; pick whichever is closest to your users or matches your data-residency preference.
Yes. Request a region migration from the dashboard and we run the move in the background. The system emails you when the migration completes; total transfer time depends on data volume but typical instances finish in a few hours. There is no extra charge for a region change.
Yes. Full data export is available at any time, in a portable format you can bring to any infrastructure.
You swap the client snippet on your forms and point your backend's verification call at your HeCAPTe instance instead of Google. Most teams change a few lines per form.
Yes. The integration shape is the same: a client widget plus a server-side verify call. You replace the vendor's keys and endpoint with your instance's site key and verify URL, and your forms keep working.
Yes. We point your chosen subdomain, for example captcha.yourdomain.com, at your instance and issue the SSL certificate.
There is a community Drupal module that wires HeCAPTe into Drupal's form protection. There is no official WordPress plugin yet. For other frameworks you call the HTTP API directly; any backend that can POST and read JSON integrates in a few lines.

03

Billing, support, and platform

€9 covers everything we do for that app: hardware in the region you choose, daily off-site backups with one-click restore, automatic security patches and version upgrades, 24/7 monitoring, SSL and firewall, and engineering support on email and the ticket section in the client portal. There are no setup fees or hidden line items. For more info see our Pricing page.
If you decide to continue, we charge €9/app/month from day 8. If you don't, the trial ends and you can export your data. No card is required for the trial, and we never auto-charge you without explicit consent.
No. The €9/month is flat regardless of how many users log into your app. Add 5 users or 50; the price doesn't change.
24/7 email and ticket support, both staffed by engineers who run the systems. We handle DNS configuration, SMTP setup, app integrations, performance tuning, troubleshooting, and migration help. Response time is typically under an hour. There is no tier system — every customer gets the same support.
Yes. Cancel from the dashboard. We don't charge a cancellation fee, we don't lock data, and we will export your data to you on request before deletion. data to you on request before deletion.
Every customer instance is backed up daily to a separate region from the primary. We test restores. You can request a restore at any backup point within the retention window — usually 7 days for daily backups.
Your application data sits in the region you choose at provisioning — 21 datacenter locations across six continents. Account-level data (billing, account email, support ticket history) is processed centrally. Application data region is picked by you, per app.
99.9% uptime SLA on every app, every tenant. Service credits are documented at danian.co/service-level-agreement. The status page is located at status.danian.co.
When your tenant approaches the resource ceiling — the base tier holds 1 vCPU/RAM, 30 GB storage — we notify you. Resource upgrades happen with your explicit consent; we will not upgrade your tenant or charge you without it.
We wait. We don't suspend the app or delete your data on the first failed charge. We email you, you fix the card on file, and we continue.
Invoices can be downloaded from the billing dashboard in PDF the day each charge succeeds. EU VAT is added where applicable and the VAT-reverse-charge regime applies for VAT-registered businesses with a valid number.
150+ open-source apps across automation, team chat, file sync, analytics, AI, password management, email marketing, dev tools, project management, smart home, CMS, and federated social. See the full catalog →
Yes. Every instance comes with a web-based terminal and a file manager in your DANIAN management dashboard. Useful for managing your data and customizations.
Resources scale with your usage. If your app needs more vCPU, RAM, or storage, we add it — and we ask first before any change to your plan. €9 is the floor; resource-heavy workloads may price higher, but you'll always know in advance.
Yes. We have both a Partner program and an Affiliate program available. Anybody can sign up.
No contract. No minimum commitment. Cancel anytime from the dashboard with one click. The 7-day free trial requires no credit card. After the trial converts to paid, you can still cancel at any month without notice or penalty.

DEPLOY IN YOUR REGION

21 datacenter locations on six continents

Pick the region closest to your users.

United States, Germany, Finland, Singapore, Australia, Brazil, Canada, Netherlands, UK, Spain, Italy, France, Sweden, Malaysia, India, Japan, Mexico, Poland, South Korea, Chile, South Africa and more coming soon
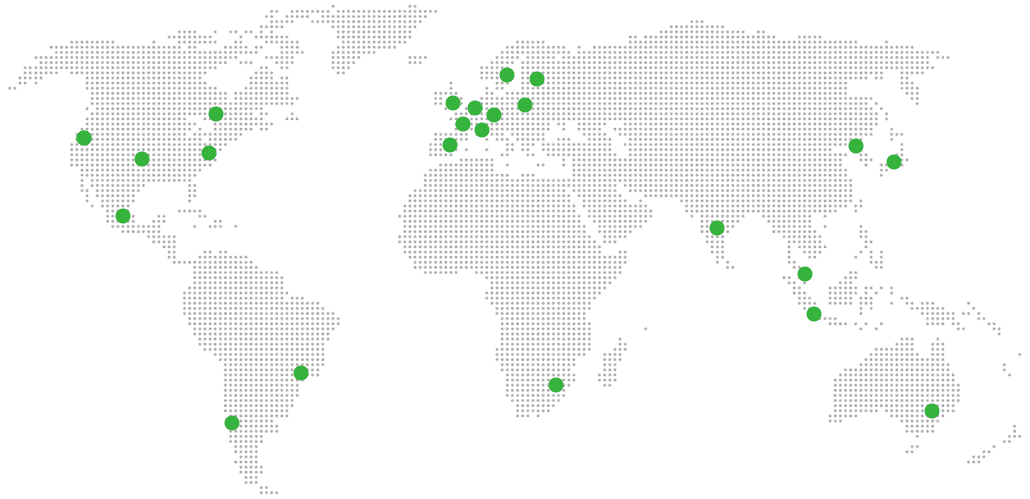
Global Reach Map

Try managed HeCAPTe for 7 days

No card. Cancel from the dashboard.